From a compromised WordPress to an operational ontology
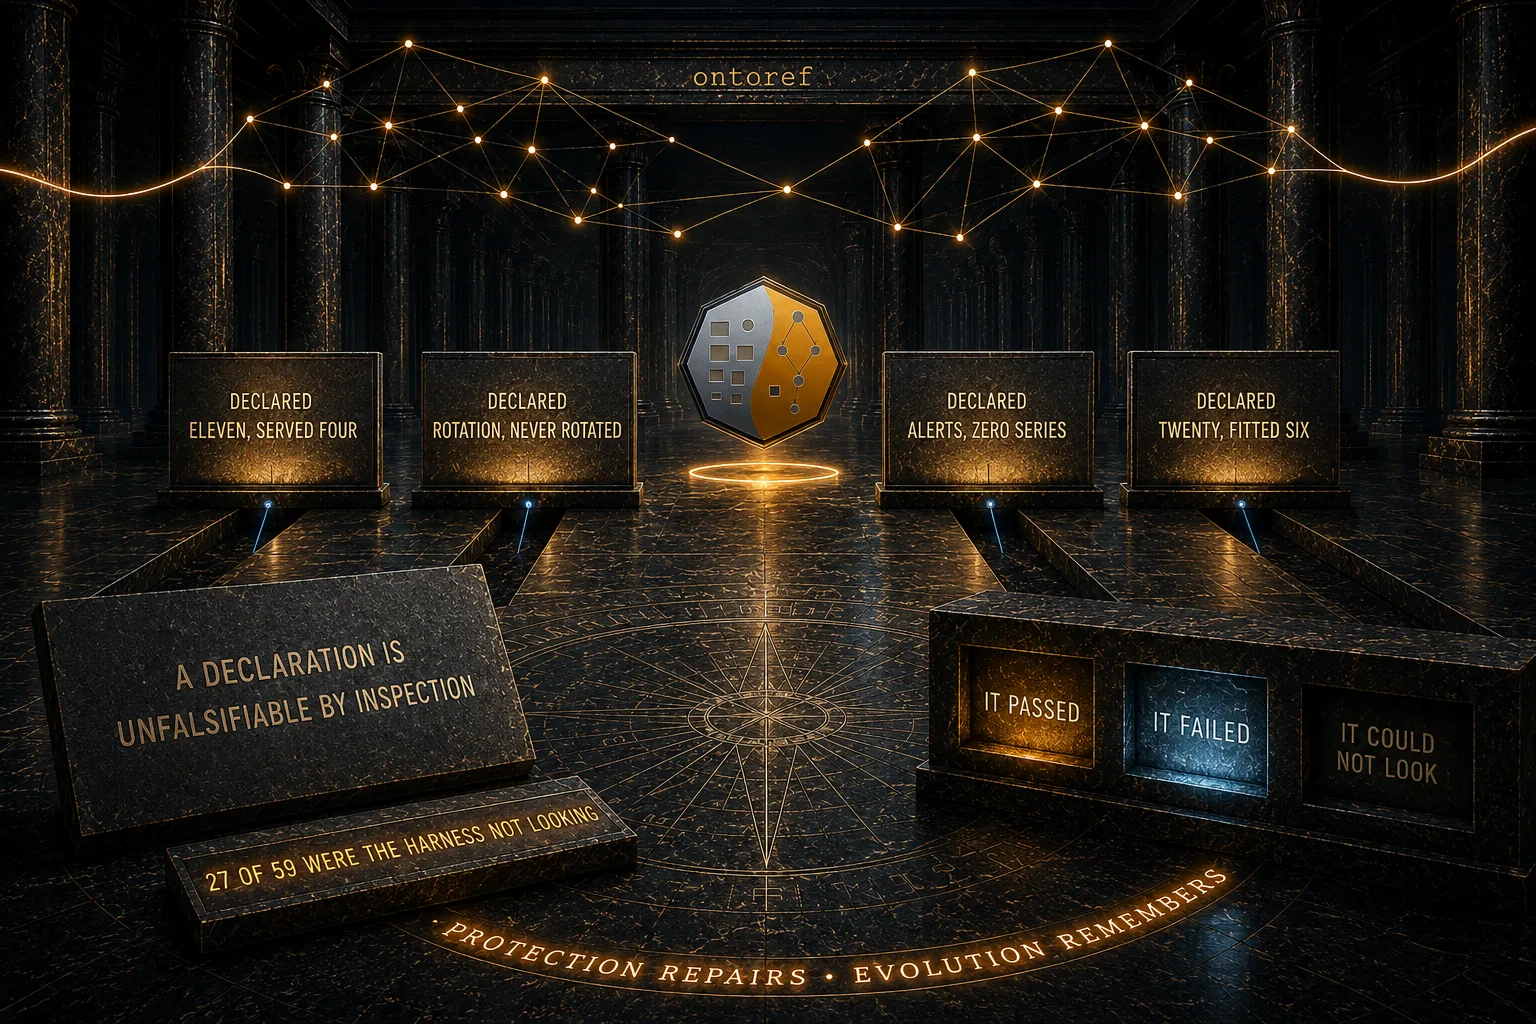
Four unrelated mechanisms were found declaring something they did not deliver — an access policy, a credential rotation, two alerts, a worker pool. None of them had failed, because nothing had ever contrasted the declaration against the running system. This post follows what came out of that: a model derived from an incident, three corrections made by the person with the operational knowledge, and a protocol decision that a check must declare what it needs in order to answer at all.
1 item